The problem: You cannot patch what you do not know you own.
The average breach starts on an asset nobody on the security team had on a list — a forgotten staging subdomain, a dev API key committed to a public repo, an IIS box someone spun up in 2019. Legacy EASM vendors will happily find those for you, then bill you per asset, so the more of your attack surface you actually monitor, the more you pay. That pricing model punishes you for being thorough.
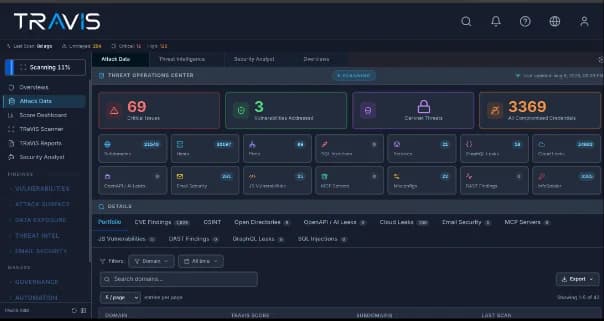
What TRaViS does: TRaViS runs continuous, attacker-perspective reconnaissance against your external footprint and tells you what is exposed, how bad it is, and what to fix first.
Domain-level asset discovery — proprietary enumeration surfaces hidden, obscure, and forgotten hostnames. Unlimited subdomains on every plan.
Exposed API key + credential detection — finds keys visible to the public and leaked logins tied to your org and employees.
Dark web + clearnet monitoring — darknet intelligence on your company, data, and staff.
Vulnerability discovery + CVE export — CVSS scoring, prioritized findings, export to CSV/JSON/print.
JavaScript & content discovery SAST — domain-wide scanning of your JS for weaknesses in code you shipped and forgot.
Google Dorks (advanced + custom) — the same OSINT queries an attacker runs, automated.
New asset detection — alerts when your footprint grows, including assets you did not authorize.
TRaViS Score — a single scored breakdown of domain security posture, plus asset classification so you can triage by business criticality.
Private Nuclei template upload — bring your own detection logic (Researcher and Enterprise).
Enterprise AI layer — AI-supplemented code fixes, root cause analysis, and per-fix vulnerability cost determination.
Nothing to install. Browser-based, works on any device, MFA on every operation, findings encrypted at rest. Integrates with the security stack you already run, and supports HIPAA, PCI, and SOC 2 evidence needs.
Built by operators, not marketers.
Comments
Publisher

seron security
Launch Date2026-10-29
Platformweb
Pricingpaid
Tags
#cyber#cybersecurity#B2B SaaS#security
Sponsors
